Secure Compute is now self-serve
By Steven Van ·
Enterprise teams can now manage Secure Compute networks and failover settings from the dashboard, API, or Terraform, no contract amendment needed.
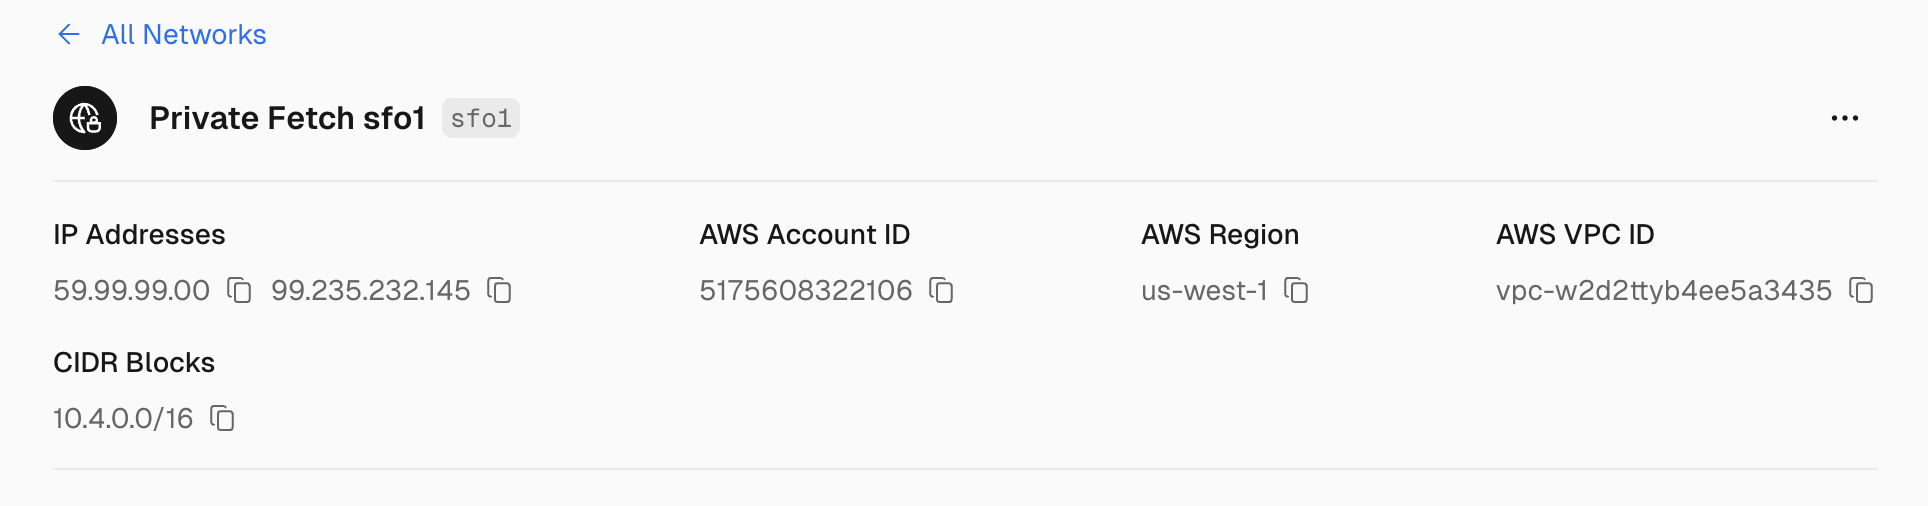
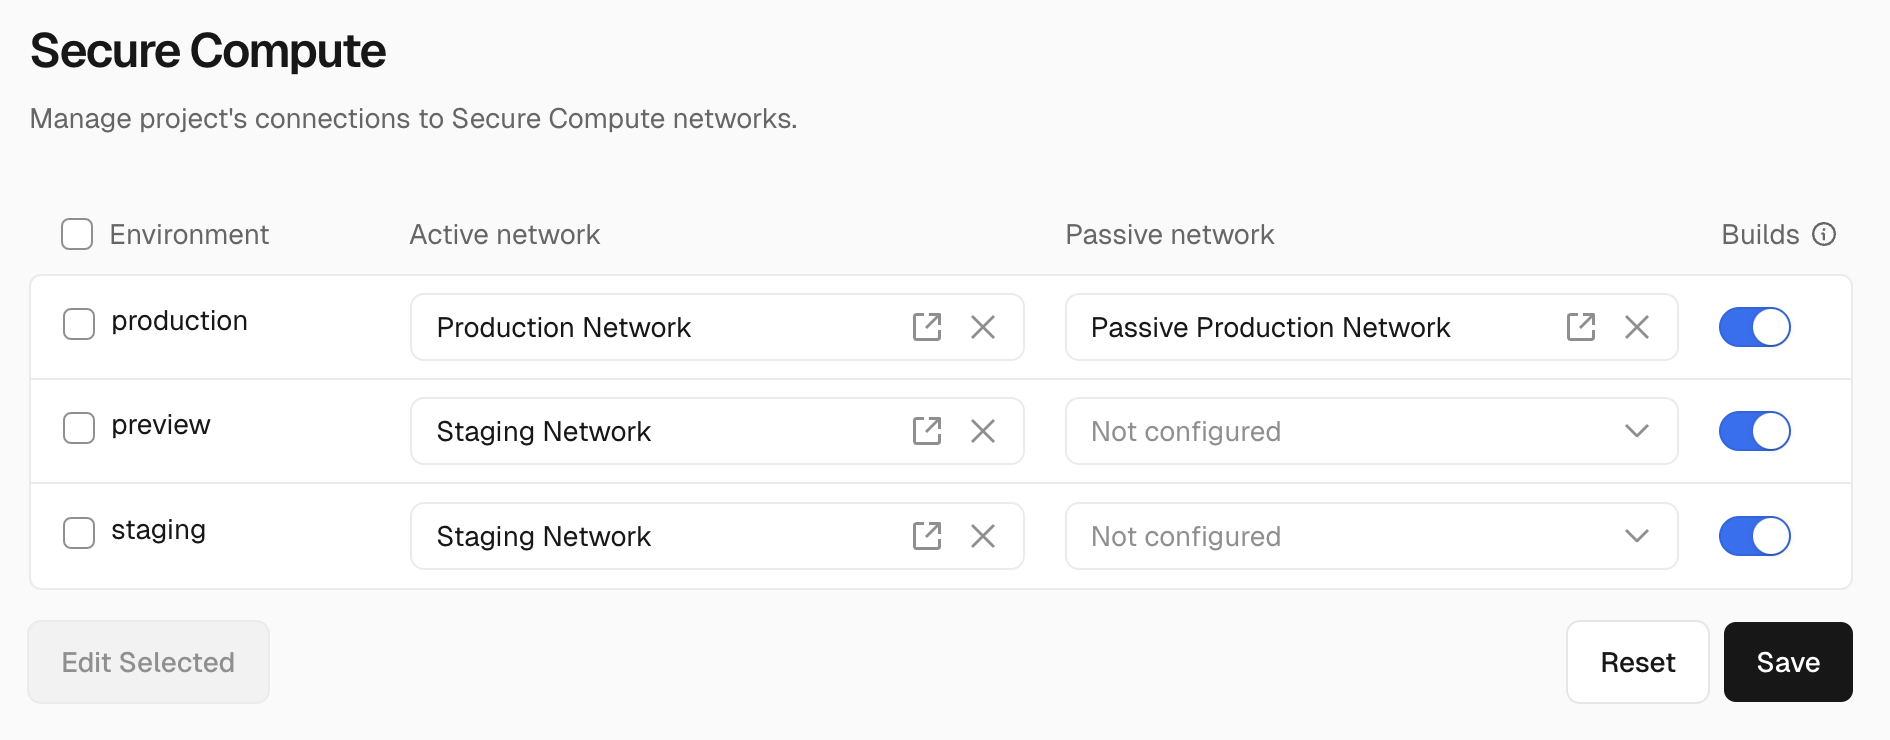
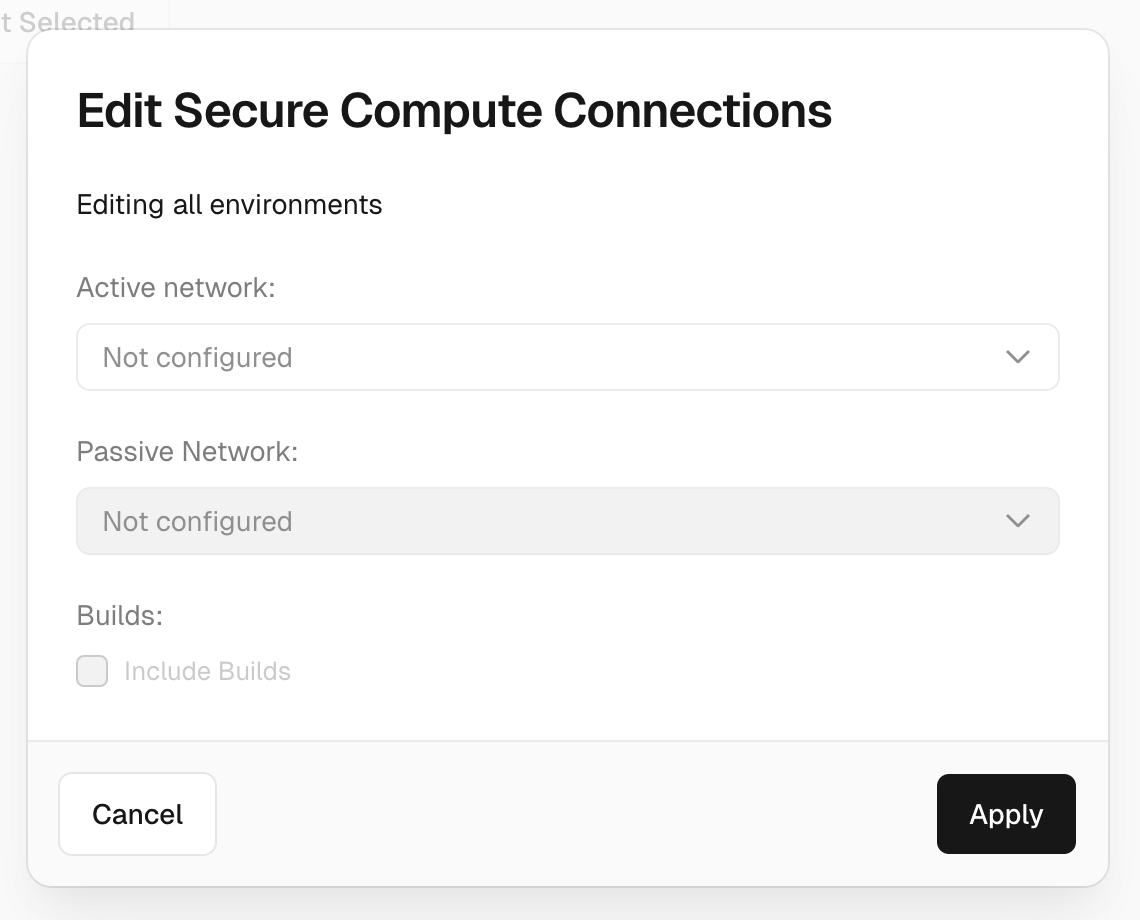
Enterprise teams using Vercel can now create, update and delete Secure Compute networks directly from the dashboard, the API, or Terraform, rather than going through a contract amendment or manual provisioning by Vercel's account team. Secure Compute networks provide private connectivity between Vercel Functions and backend infrastructure, and self-serve management now covers:
- Region and Availability Zone selection
- Active/passive failover configuration
- Private CIDR selection
- NAT and egress behaviour
Networks can be managed interactively through the dashboard or declaratively via the API and Terraform. Self-serve Site-to-Site VPN connections, Secure Compute for Pro customers, and PrivateLink connectivity are coming soon. See the announcement for details.