Stage-only npm tokens for safer automation
By Steven Van ·
Stage-only npm tokens let automation submit a package version while a maintainer approves the actual publish with 2FA.
npm granular access tokens now support a Read and write (stage only) permission on GitHub. A token with this permission can submit a package version with npm stage publish, but cannot publish it directly: a maintainer must review the staged version and approve it with two-factor authentication before it goes live. Direct npm publish attempts are rejected even if the token is configured to bypass 2FA for automation.
- Stage-only tokens keep other write permissions, including moving dist-tags and deprecating versions, so they still need the same handling as other write tokens.
- The change is opt-in and does not affect existing tokens or their direct-publish ability.
- It gives teams that can't yet move to trusted publishing a migration path ahead of npm's planned removal of direct publishing via bypass-2FA tokens, targeted for January 2027.
- Staged publishing requires npm CLI 11.15.0 or later, Node.js 22.14.0 or later, an existing published package, and 2FA enabled on the account.
Full details are in npm's staged publishing documentation.
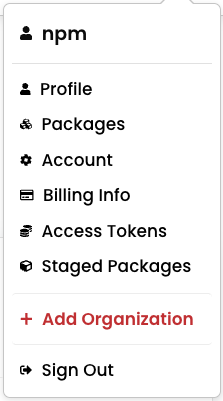
The Staged Packages tab on npmjs.com listing packages awaiting review
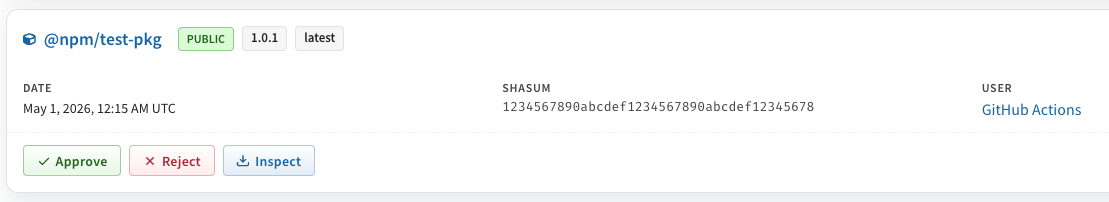
A staged package on npmjs.com with the Approve button for release
GitHub
Where the world builds software — Git hosting, pull requests, issues, Actions CI/CD, and Copilot, free for public and private repos.
View GitHub →