Base44 adds a workspace-wide Security Center for Enterprise
By Steven Van ·
The panel scans and ranks vulnerabilities across every app in a workspace, with drill-down per app and optional Wiz scanning.
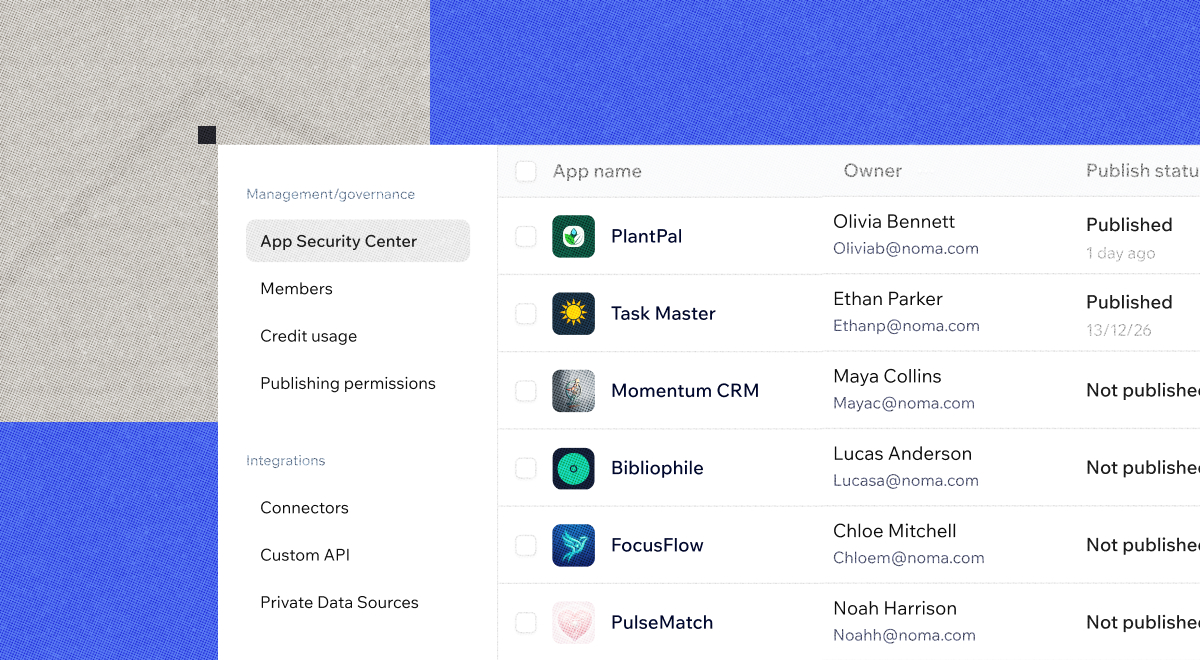
Base44 just gave security and IT teams the thing they have been asking every vibe-coding platform for: a single place to see the risk across everything their company is building. The new Security Center scans and monitors every app in a workspace from one panel, ranks vulnerabilities by severity, and lets you drill down into any single app. It opens from the admin sidebar and is available on Enterprise workspaces.
One panel for a hundred apps
The core problem Security Center solves is scale. Base44's pitch is that anyone in a company can describe an app and ship it, and enterprises that adopt it end up with dozens or hundreds of internal tools built by people who are not engineers. Until now, checking those apps meant opening them one at a time. Security Center flips that: the whole workspace is scanned and monitored from a single view, with issues ranked by severity so a security lead sees where to focus first. From the workspace-level view you can drill into any individual app to see exactly what was flagged and where.
Base44's framing in the announcement is the right one: teams keep building, you keep oversight. Governance tools like this are what decide whether an IT department blesses a platform or bans it, and the severity ranking is the practical detail that makes the panel usable rather than just another wall of alerts.
Built on Base44's existing security scanning
Security Center sits on top of scanning machinery Base44 already runs per app. Its built-in security scan analyzes app code for the issues that actually plague AI-generated apps: hardcoded secrets like exposed API keys, missing row-level security that lets users read records they should not, and backend functions without proper server-side authentication. Base44's own documentation notes that exposed secrets, missing database access controls, weak auth configuration, and missing security headers account for the large majority of vulnerabilities found in apps on the platform.
Enterprise workspaces can also connect a Wiz tenant, in which case scans additionally run Wiz software composition analysis and static application security testing, surfacing vulnerable dependencies and risky code alongside Base44's built-in checks. Security Center becomes the roll-up view across all of it.
Why enterprise governance is the current battleground
Base44, acquired by Wix in 2025, has been shipping steadily toward enterprise legitimacy: workspace administration, a public trust center, OWASP-based penetration testing, and a bug bounty program. Security Center is the natural next step, because the biggest objection to letting non-developers build production software has never been capability, it has been oversight. A ranked, workspace-wide vulnerability panel is a direct answer to the CISO question of "how do I know what all these apps are doing?"
How to get it
If you are on an Enterprise workspace, open Security Center from the admin sidebar. If your company is evaluating Base44, this feature belongs in the security review conversation: it is the difference between auditing apps one by one and seeing the whole estate at once.